- Who this helps
- Tourism internal auditors, quality managers and process owners.
- What you can do
- Assess currency, understanding, execution, records and effectiveness using an evidence-led audit approach.
#The operating problem
An SOP audit asks whether the controlled arrangement works in practice. The auditor follows requirements, work, records, people, systems, exceptions, measures, and outcomes to determine conformity and effectiveness—not whether a polished PDF exists. The strongest audit conclusion also states the limits of the evidence, because a defined sample supports judgment without pretending to prove every service, shift, location, or supplier behaved identically. Tourism operations are unusually exposed at interfaces. Sales may define the promise, Reservations holds changing information, Operations coordinates capacity and decisions, suppliers provide critical resources, field teams face the guest, and Finance or the client needs evidence afterward. A control that works inside one department can still fail at the handoff, during a change, or outside office hours. The method in this article is therefore designed as part of an end-to-end operating system. The wider architecture is explained in the tourism-company operating system, while the document-type comparison separates policies, SOPs, work instructions, checklists, forms, templates, and records. That distinction matters because a management method should generate the right controls and evidence rather than forcing every requirement into one document. This is a practical interpretation for tourism management, not a claim that any cited framework prescribes the exact template shown here. The organization remains responsible for tailoring terminology, depth, approval, safety, privacy, employment, contractual, financial, accessibility, regulatory, emergency, and records controls to its jurisdiction, services, risks, technology, and competence.
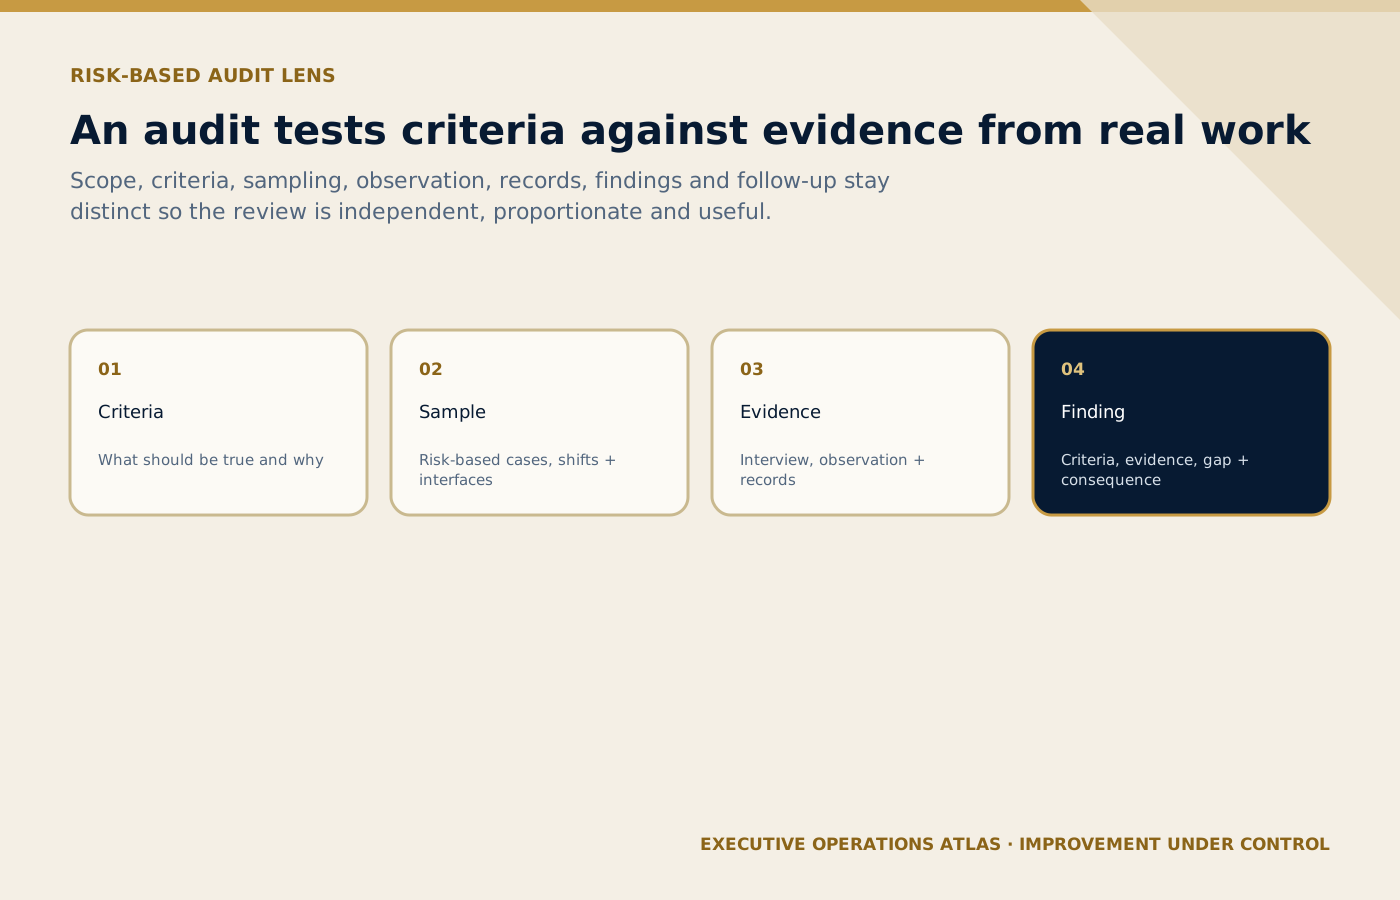
A finding becomes credible when the selected sample and corroborated evidence can be traced directly to defined criteria.
On small screens, scroll the diagram horizontally to read its labels.
#Concepts that must stay distinct
Audit criteria define what the evidence is compared with: the current SOP, applicable policy, contract, law, risk control, service standard, or other approved requirement. Auditors should not convert preference into a finding. Objective evidence may include observation, records, interviews, system data, test results, physical conditions, and traceable communications. One source rarely tells the whole story; triangulation helps distinguish an isolated account from a systemic condition. Sampling creates reasonable insight within a defined scope; it does not prove that every service conformed. The audit record should explain population, period, risk basis, sample method, limitations, and any expansion triggered by emerging evidence. Independence is proportionate, not theatrical. An auditor should be sufficiently free from responsibility for the work being audited to make an impartial judgment, while still understanding tourism operations well enough to recognize meaningful evidence.
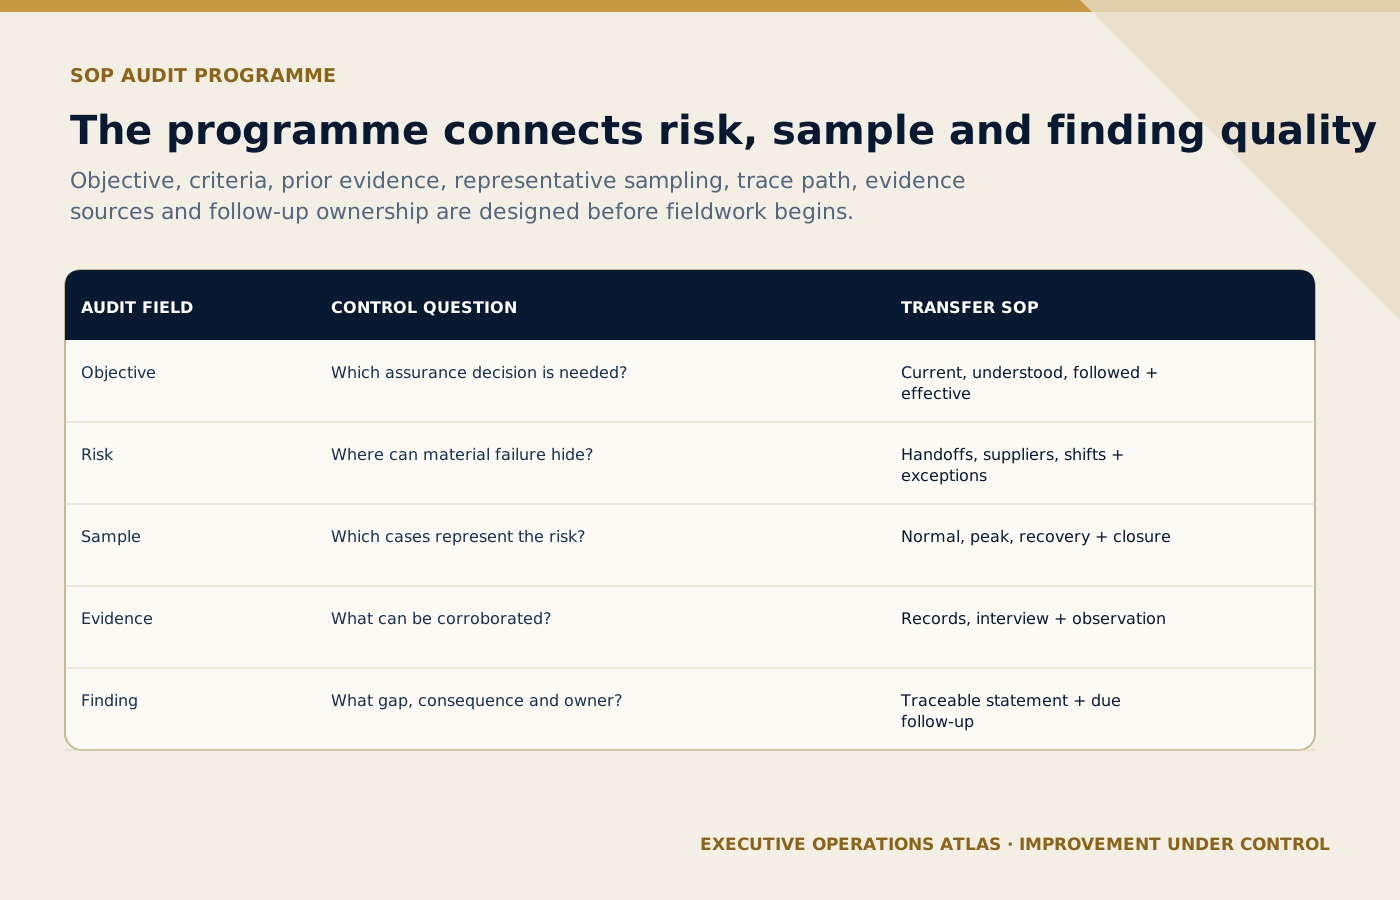
Risk and prior evidence determine where the audit looks, which service references it follows and how findings will be supported.
On small screens, scroll the diagram horizontally to read its labels.
#Practical tool: Risk-based SOP audit programme, sampling sheet, and finding test
Use the following canvas in a working session with a current process, representative service records, and the people who perform or receive the work. Mark assumptions and missing evidence openly; a blank or disputed answer is more useful than a confident invention.
| Element | Management question | Tourism application |
|---|---|---|
| Exists and current | Is the approved SOP identifiable and available? | Owner, version, effective date, access, withdrawn copies |
| Competence | Do affected roles understand and demonstrate it? | Training, observation, decisions, deputy coverage |
| Conformity | Is the required work followed? | Normal and exception samples across shifts and partners |
| Evidence | Do records show what happened? | Inputs, timestamps, authority, communication, closure |
| Performance | Do measures and outcomes support effectiveness? | Delays, defects, complaints, recurrence, recovery |
| Suitability | Does the control still fit the operation? | System, supplier, airport, contract, risk, or service change |
Scroll horizontally to read every column. Keyboard: focus the table, then use the arrow keys.
What to learn: Read each row across to connect Element with Management question, Tourism application. Compare the rows to identify the relevant element for your situation; use the accompanying section to interpret the result.
The canvas is intentionally compact. Its output should link to the controlled source—process map, risk register, requirement, data definition, SOP, system rule, supplier interface, training record, test, dashboard, audit, or improvement case. Copying detail into several places creates the appearance of completeness while weakening change control.
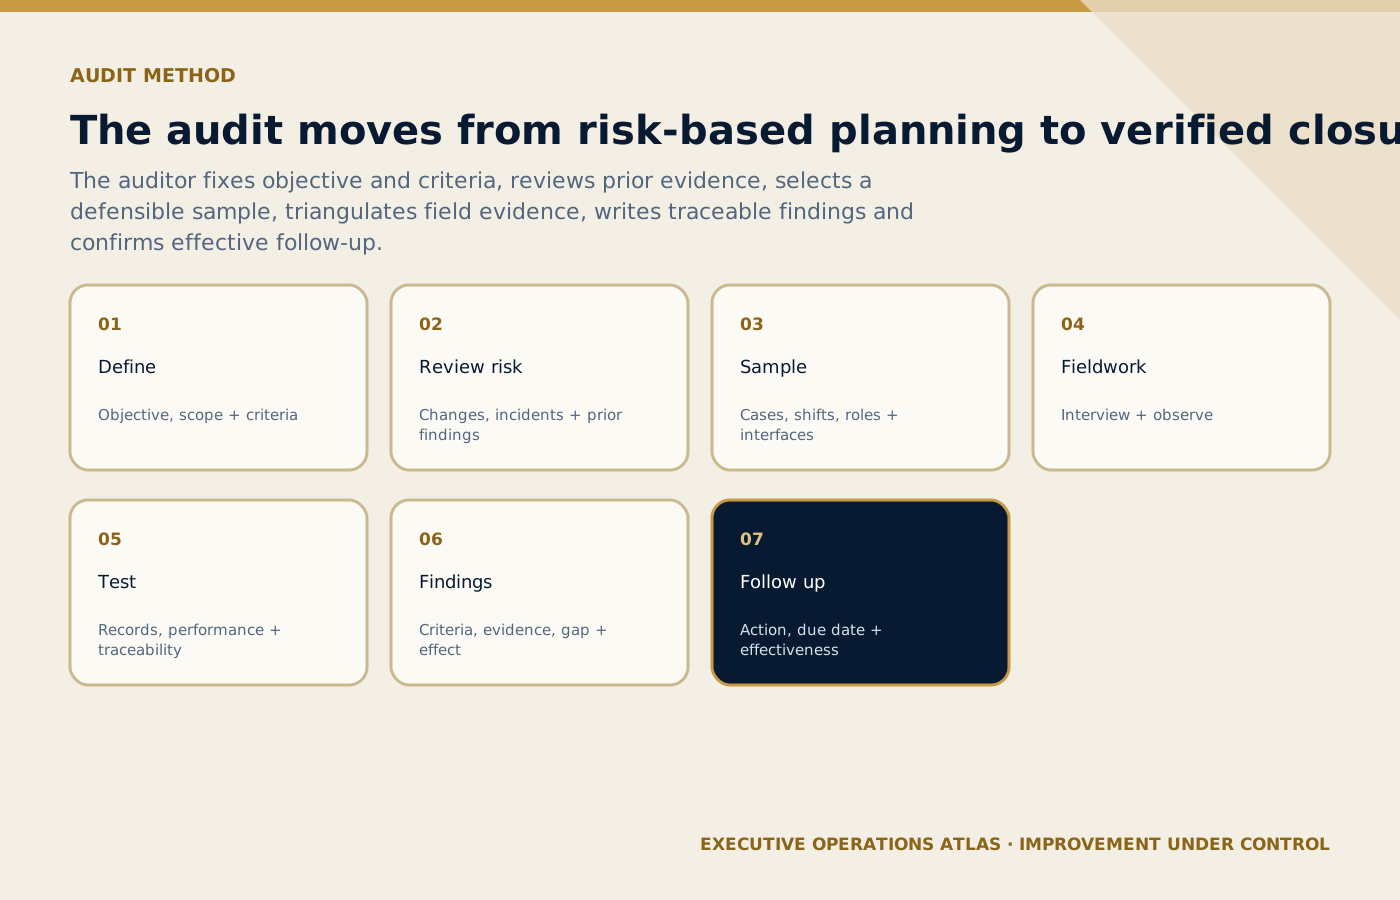
The audit moves from a defensible plan through triangulated field evidence to findings whose effectiveness can be independently verified.
On small screens, scroll the diagram horizontally to read its labels.
#A professional method
#Define objective, scope, and criteria
State why the audit is being performed, which locations, services, periods, roles, partners, systems, and SOP versions are included, and the exact criteria used for judgment.
#Review risk and prior evidence
Examine complaints, incidents, KPIs, change records, prior findings, CAPA, STPs, and management concerns. Use them to focus the plan without presuming that a concern is already a finding.
#Design the sample
Select normal and exception cases across time, service type, shift, supplier, and outcome. Include trace-forward and trace-backward samples so records can be connected from booking to closure and from complaint to source.
#Conduct interviews and observation
Ask roles to explain and demonstrate the work in their own environment. Use open questions, follow evidence, and distinguish a person not remembering document language from a genuine control failure.
#Test records and performance
Compare required inputs, steps, decisions, evidence, time thresholds, escalation, and closure with actual cases. Reconcile system data and retained messages where they form part of the approved record.
#Write evidence-based findings
Identify the criterion, objective evidence, observed gap, scope, and risk. Separate conformity, observation, opportunity, and nonconformity according to the organization's audit method.
#Close and follow up
Agree factual accuracy, assign action ownership through the CAPA process, track due dates, and verify effectiveness rather than accepting a revised document as automatic closure.
At the end of the method, require a decision backed by evidence: proceed, proceed conditionally with named controls, return for correction, or stop. Record the decision maker, date, scope, residual issues, and next review. Ambiguous approval is especially dangerous in tourism because live teams and partners will fill the gap differently under time pressure.
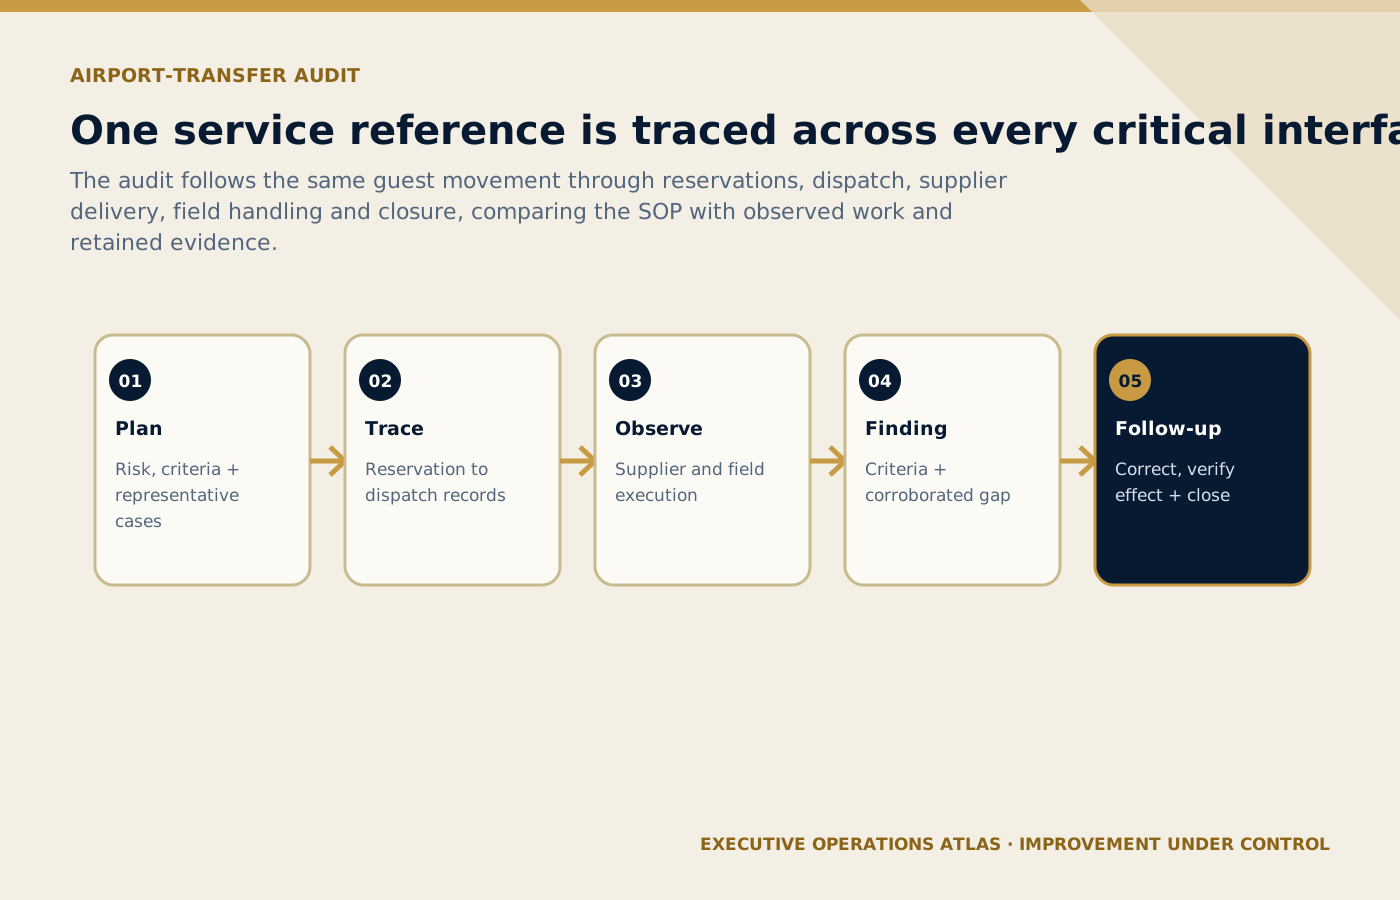
One service reference is followed across every critical interface so the audit tests real operational continuity rather than document presence.
On small screens, scroll the diagram horizontally to read its labels.
#Example: Auditing an airport-transfer SOP end to end
Illustrative scenario
Operational teaching scenario, not a documented incident. Uncited figures and outcomes are illustrative assumptions.
- Situation
An airport-transfer SOP needs an end-to-end audit of execution, evidence and service closure.
- Evidence
Check the approved service brief, current passenger count, confirmed vehicle and driver, access conditions, deadlines and activation authority.
- Decision
Decide whether to release, wait, reroute or activate the approved backup using verified readiness and the stated decision deadline.
- Action
#Plan
The auditor defines a four-week population of arrival transfers and selects normal services, changed flights, no-shows, supplier substitutions, and one complaint across day and night shifts.
#Trace
Each sample is followed from confirmed service order through assignment, readiness, live status, guest contact, completion, evidence, and any exception decision.
#Observe
A dispatcher demonstrates the current screen and escalation route. The process works, but the printed night-shift contact list is a withdrawn version not governed by the system.
#Finding
The report cites the current-access and withdrawal requirement, the observed uncontrolled list, its location and version, and the risk of using an obsolete escalation contact. It does not accuse staff of carelessness.
#Follow-up
The owner removes obsolete copies, changes the access method, briefs affected shifts, samples night-time use, and proves that the control remains effective after several weeks.
The example is not a universal SOP. A company should repeat the reasoning with its own service promise, systems, suppliers, volumes, guest profiles, legal environment, and disrupted conditions. Compare the design with operational risk assessment and customer-journey mapping for SOP design so operational control, risk, and the visible guest journey remain connected.
#Common failure modes—and the management response
- Auditing only the sop file. Trace the operational consequence using a recent case, then identify the earliest control that could have prevented, detected, or safely contained the condition.
- Asking leading questions and treating agreement as evidence. Follow the issue across upstream inputs and downstream handoffs. The visible lapse may originate in workload, information, authority, system design, supplier behavior, or an incentive outside the user's control.
- Sampling only convenient successful cases. Decide whether the remedy belongs in process design, the SOP pack, technology, resource planning, supplier governance, competence, or leadership policy. Adding prose to the wrong document will not control the cause.
- Writing findings without criteria. Test the proposed remedy in a normal case and a credible exception. Confirm that improvement in one measure has not transferred delay, risk, cost, or confusion to another role or the guest.
- Confusing advice with nonconformity. Assign one accountable owner, evidence, due date, and review point. An informal workaround may protect today's service but should not silently become the future operating method.
- Closing action when a document is edited but behavior is unverified. Record the residual risk and escalate it through the approved route. A vague warning such as ‘take care’ is not an observable control and cannot support an effectiveness decision.
- Verification
Reconcile the physical count with the movement record, confirm the receiving team’s handover and keep unresolved passengers or tasks open.
#Implementation roadmap
Implementation should be proportionate to risk and change. The same five gates can govern a small improvement or a cross-company launch, but the evidence, independence, resources, testing, and approval depth should match the potential consequence.
#Phase 1: Mandate
Confirm sponsor or owner, scope, authority, success criteria, affected stakeholders, risk, resources, and the evidence required before proceeding. Put unresolved assumptions in an issue log rather than disguising them as approved facts.
#Phase 2: Design
Use observed work, representative records, customer and partner needs, data, risk, and front-line knowledge. Align the method with process maps, SOPs, systems, contracts, supporting tools, roles, and existing governance.
#Phase 3: Pilot
Choose representative normal, boundary, and exception cases. Protect live operations, define acceptance and stop criteria in advance, record actual results, correct defects through control, and retest affected interfaces.
#Phase 4: Release
Verify approved content, access, system readiness, partner acknowledgement, competent users, supervisor coverage, communications, rollback or contingency, monitoring, support, and explicit go-live authority.
#Phase 5: Sustain
Review early use, compare results with baseline, audit deployment and effectiveness, route recurrence through RCA and CAPA, preserve lessons, and control revisions so improvement does not create parallel versions.
Control the approved version through document control and version management. Use training, competency, and SOP adoption to verify competence and adoption rather than counting distribution or attendance. Where suppliers perform part of the process, apply the interface and performance disciplines in supplier and partner governance.
#Measures that support decisions
Select a small balanced set. For each measure define purpose, formula or classification rule, numerator and denominator where applicable, source, owner, refresh, segmentation, target, response threshold, and known limitations. A measure without an action route becomes reporting overhead.
| Measure | Decision use |
|---|---|
| Audit programme delivered by risk priority | Shows whether the method is deployed, producing its intended result, exposing risk early, or requiring investigation and controlled improvement |
| Samples with complete traceability | Shows whether the method is deployed, producing its intended result, exposing risk early, or requiring investigation and controlled improvement |
| Findings supported by criterion and evidence | Shows whether the method is deployed, producing its intended result, exposing risk early, or requiring investigation and controlled improvement |
| Actions closed by due date | Shows whether the method is deployed, producing its intended result, exposing risk early, or requiring investigation and controlled improvement |
| Repeat findings by process | Shows whether the method is deployed, producing its intended result, exposing risk early, or requiring investigation and controlled improvement |
| Effectiveness checks passed after closure | Shows whether the method is deployed, producing its intended result, exposing risk early, or requiring investigation and controlled improvement |
Scroll horizontally to read every column. Keyboard: focus the table, then use the arrow keys.
What to learn: Read each row across to connect Measure with Decision use. Compare the rows to identify the relevant measure for your situation; use the accompanying section to interpret the result.
Read the measures together. A better average can hide a damaging tail; a lower complaint count can reflect harder reporting; a perfect checklist score can coexist with weak outcomes; and a rise in recorded exceptions may be healthy when previously hidden problems become visible. Segment results and combine performance data with observation, audit, guest evidence, supplier context, and front-line feedback.
#Field review before approval
#Value and outcome
Can the team state which guest, client, employee, partner, or organizational outcome this method protects, and what evidence would show that value was actually created? Review one successful and one failed service so internal completion is not confused with customer value.
#Boundary and ownership
Are trigger, completion, exclusions, process owner, deputies, and connected services explicit? Follow one service reference end to end and note every point where work crosses a department, system, shift, location, or supplier boundary.
#Risk and resilience
Have credible failure, peak demand, absence, conflicting information, technology loss, supplier failure, accessibility need, and recovery been examined proportionately? Confirm that efficiency does not remove the capacity or discretion needed to stabilize a disrupted service.
#Data and evidence
Are definitions, sources, timestamps, versions, calculations, access, corrections, and retention controlled enough to support the stated decision? Reconstruct an event from records and identify any conclusion that depends on memory, a private message, or an unverified field.
#People and authority
Can representative users explain and demonstrate their role, decision limits, handoffs, and escalation under real working conditions? Include night, weekend, remote, temporary, and partner personnel where they form part of the service.
#Guest and partner interface
Does the design control what external parties need to know, provide, acknowledge, decide, and record without exposing them to contradictory instructions? Walk through the visible guest experience and ask a partner to demonstrate the handoff in their own words.
#Usability and technology
Can the method be used on actual devices, channels, locations, languages, and workload conditions without unofficial notes or coaching? Observe searching, scrolling, duplicate entry, screenshots, manual workarounds, and automation failure as evidence about design.
#Learning and governance
Will incidents, complaints, defects, tests, audits, measures, user feedback, supplier signals, and external change reach a named review and controlled decision? Distinguish urgent correction, formal CAPA, routine revision, project change, and strategic improvement.
#How this article connects to the series
The most useful connected articles are document control and version management, CAPA for tourism operations, tourism KPIs and control dashboards. Each supplies a prerequisite, complementary control, or next improvement step; the links form a deliberate route through the series rather than promotional references added after drafting. The existing portfolio demonstrates the operating context in From Airport Arrival to Final Farewell, The Abu Dhabi MICE Movement Control Room, The Tourism Quality and SOP AI Toolkit. Those pieces show journeys, assignments, control rooms, dashboards, guide quality, AI tools, commercial workflows, or recovery in practice. This article adds the management method behind repeatable delivery.
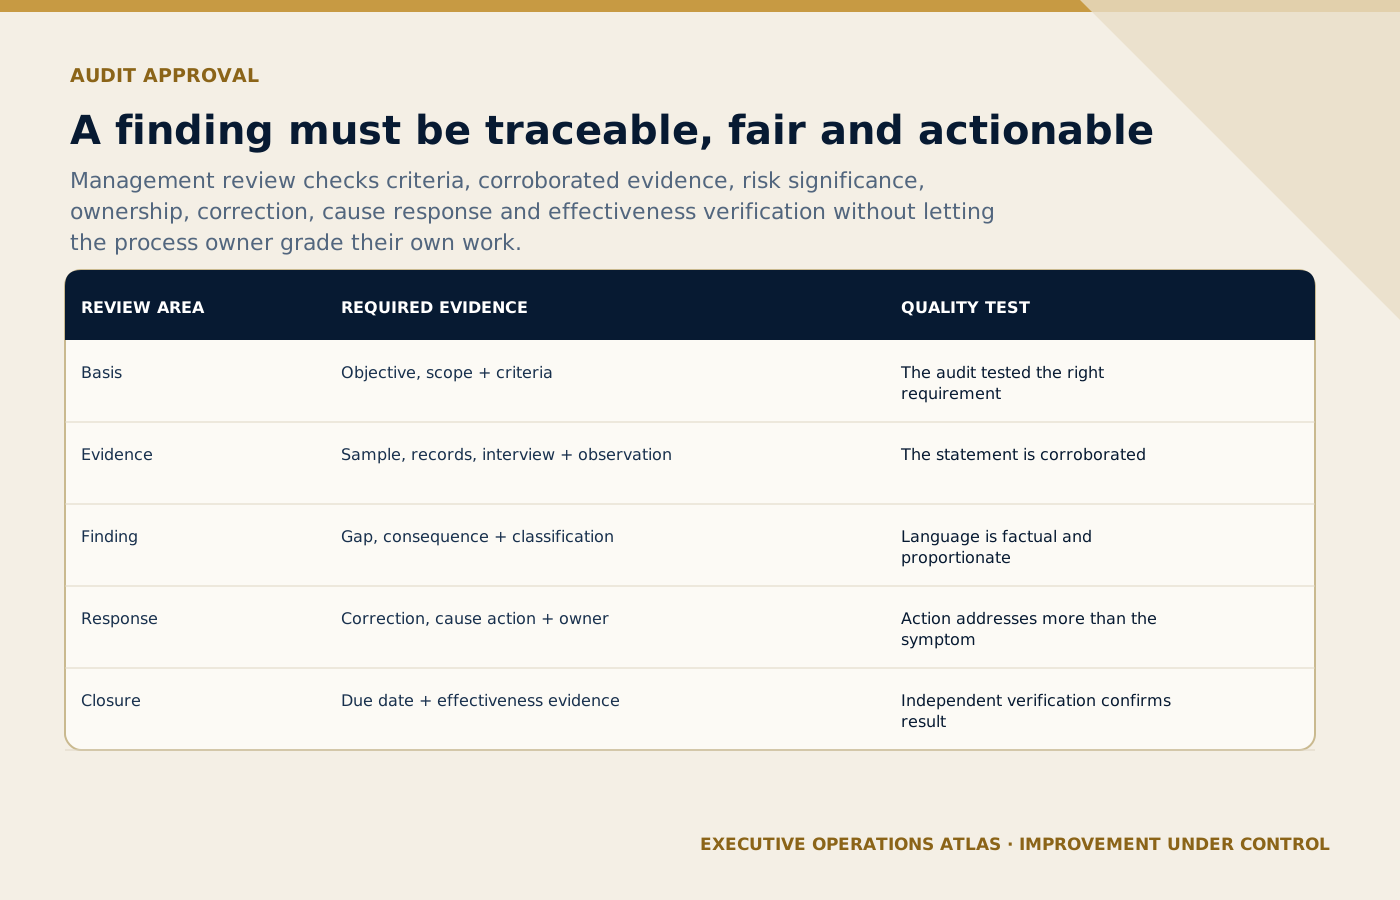
Management accepts a finding when it is factual and proportionate, then closes it only after independent effectiveness evidence.
On small screens, scroll the diagram horizontally to read its labels.
#Manager's approval checklist
- The purpose, service value, scope, owner, users, authority, and required outcome are explicit.
- The method reflects observed work, current systems, representative data, guest needs, partners, risk, and disrupted conditions.
- Definitions, roles, thresholds, evidence, privacy, accessibility, safety, exceptions, and escalation are controlled at the appropriate level.
- Supporting documents, systems, tools, contracts, training, tests, dashboards, and records agree with one another.
- Representative users and partners have demonstrated the design in normal and exception scenarios without hidden coaching.
- Release, access, version, support, monitoring, audit, change, retention, improvement, and withdrawal arrangements are ready.
#Sources and further reading
Primary standards, institutional guidance and professional references used to support this article.
- ISO 19011:2026 — guidelines for auditing management systems
- ISO 10013:2021 — guidance for documented information
- ISO 9004:2018 — guidance for sustained organizational success
- ISO 31000:2018 — risk management guidelines
Editorial note: This article provides operational and quality-management guidance for a professional portfolio. It does not provide legal, regulatory, privacy, safety, emergency, employment, financial, or contractual advice, nor does it replace official framework training or certification materials. Apply qualified local review wherever those obligations affect the service.
Connect this guide to your next step
Continue with related methods and the wider series.
- Related guideCAPA: Corrective and Preventive Action in Tourism
Turn complaints, incidents, audit findings, defects, and adverse trends into controlled actions that contain the problem, remove verified causes, and prove the change works.
- Related guideThe Integrated SOP Creation Model: ITIL + PMP + Lean Six Sigma
Combine service value, project delivery, flow, variation, documented information, risk, testing, competence, measurement, audit, and improvement into one practical SOP lifecycle.
- Related guideWhere Does STP Fit? Standard Test Procedures in Tourism Operations
Separate instructions for doing the work from controlled tests that prove the process, system, handoff, or contingency performs as intended.
Put this article into practice
- Assess currency, understanding, execution, records and effectiveness using an evidence-led audit approach.
- The purpose, service value, scope, owner, users, authority, and required outcome are explicit.
- The method reflects observed work, current systems, representative data, guest needs, partners, risk, and disrupted conditions.
- Definitions, roles, thresholds, evidence, privacy, accessibility, safety, exceptions, and escalation are controlled at the appropriate level.
Your next step
Use this connected method when you are ready to build a CAPA workflow that separates containment, verified cause, corrective action and effectiveness checks.
Review CAPA: Corrective and Preventive Action in Tourism